Trust and security
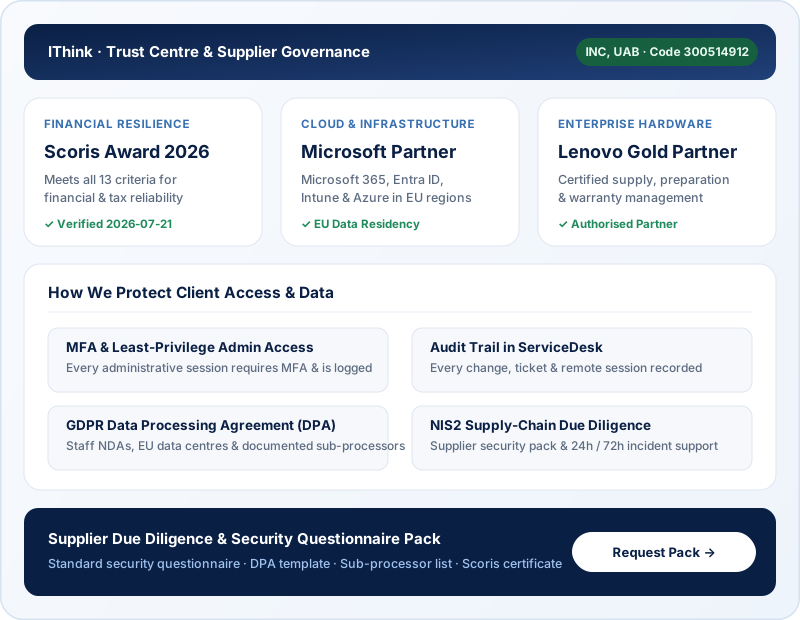
An IT provider gets access to your systems, so trust has to be shown, not claimed. Here is how we handle your access and data, and how we can support your supplier due diligence.
Recognition and partnership
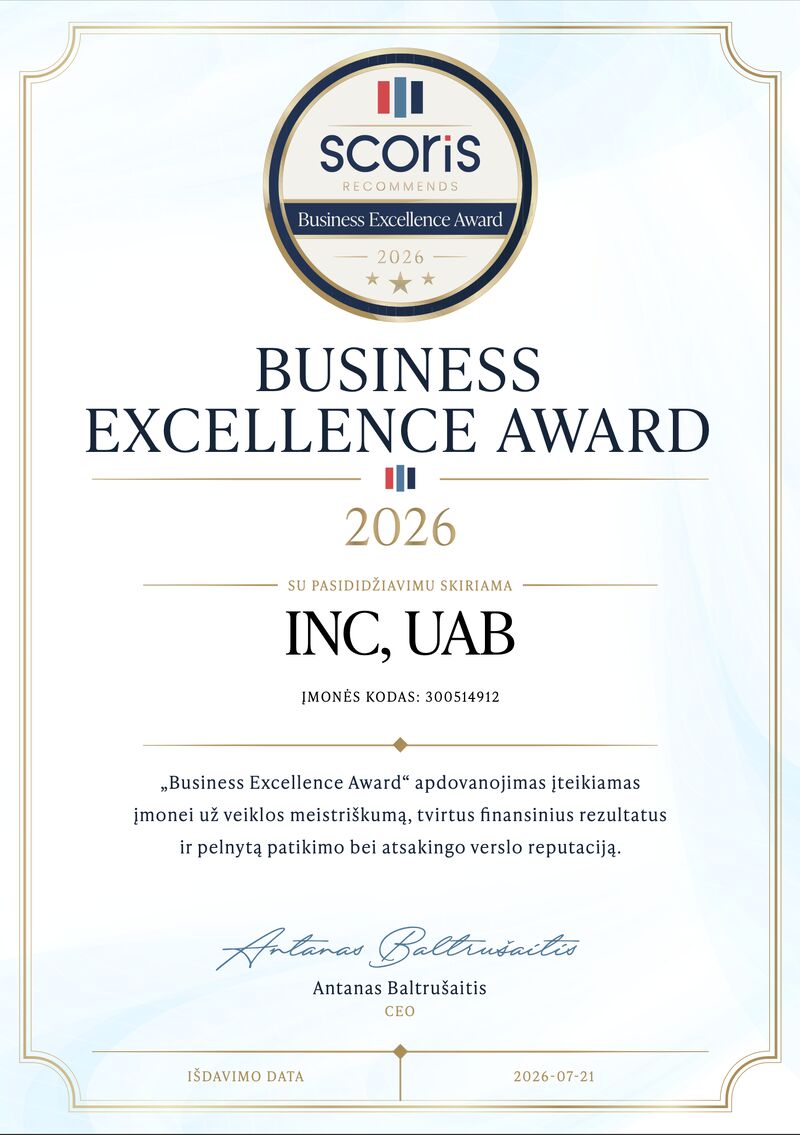
Scoris Business Excellence Award 2026
Scoris grants this award to companies that meet all 13 criteria for financial resilience, tax compliance and business reliability. It is independent evidence that IThink is a stable, reliable supplier, which matters in supplier due diligence, including NIS2 supply-chain checks.
Issued 21 July 2026 · INC, UAB, company code 300514912
Microsoft partner
Lenovo Gold Partner
IThink is a Lenovo Gold Partner: we select, supply, prepare and support Lenovo computers, servers and accessories for business – with the manufacturer’s warranty and our help with warranty cases. IT hardware
How we protect your access
We connect to your systems securely and only as far as the work requires, and we manage access across each employee’s time with your company.
- Multi-factor authentication (MFA)
On all administrative access. - Manage access from joining to leaving
New starters get access from day one; leavers lose it straight away. - Only the access people need
Everyone gets only the access their job requires. - Activity logging
Work is recorded in our ServiceDesk. - Controlled remote access
Secure remote-connection tools.
Incidents, data and people
Incident notification
If a security incident may affect your systems or data, we notify your contact person without delay, and no later than 24 hours, and help you meet the NIS2 and GDPR reporting deadlines (24 h / 72 h).
Data in the European Union
Our core systems – Microsoft 365 and our ServiceDesk (Autotask) – run in EU data centres, and backups we hold for you are stored in the EU. Where a provider may access data from outside the EU, the European Commission’s standard contractual clauses apply.
Staff confidentiality
Every employee signs a confidentiality (NDA) undertaking, and we check each person’s background before hiring them.
Our own backups
IThink’s own systems – ServiceDesk, documentation and password vault – are backed up regularly and stored separately, and we test a restore twice a year.
Sub-processors
When providing IT services, we may process your data using the providers below. The final list is part of the data processing agreement (DPA).
| Provider | Purpose | Data location |
|---|---|---|
| Microsoft Ireland Operations Limited | Microsoft 365: e-mail, documents, collaboration | EU |
| Kaseya / Datto (Autotask) | ServiceDesk, client portal, IT asset records | EU |
| Kaseya | Remote monitoring, management and access | EU |
| Chosen to fit each client’s needs | Backup storage (where we hold the backups) | EU |
| Cloudflare, Inc. | Website, storage of form requests | EU / global network (standard contractual clauses) |
Documents and compliance
GDPR and data processing agreement
We provide a data processing agreement (DPA) on request.
NIS2 supplier checks
We help answer your and your customers’ security questionnaires.
Learn moreFinancial reliability
Scoris Business Excellence Award 2026 – an independent rating of financial resilience and business reliability.
Security questionnaire pack – on request
Assessing IThink as a supplier? We’ll send a pack tailored to your due diligence – we have several, depending on the client’s needs and requirements. It can include a completed security questionnaire, a description of our security measures, a DPA template, the sub-processor list and the Scoris certificate.
Report a vulnerability
Found a security issue in our systems? E-mail info@ithink.lt – we reply by the next business day. Contacts for security researchers are also published in our security.txt file.